Key Takeaways
- Recurring wallet activity suggests automated laundering of stolen assets.
- Stolen Binance assets mixed with funds from September’s Bitget theft.
- Attackers exchanged $325 million in stablecoins for $285 million in ether.
Thousands of Transfers Point to Automated Laundering
Blockchain analytics firm Chainalysis identified suspected automated laundering on Oct. 30 after a Binance theft it estimated at $6.4 billion, which it called the largest crypto theft on record. The company stated:
“Our investigators are observing never-seen-before laundering patterns with the stolen funds from the Binance exploit.”
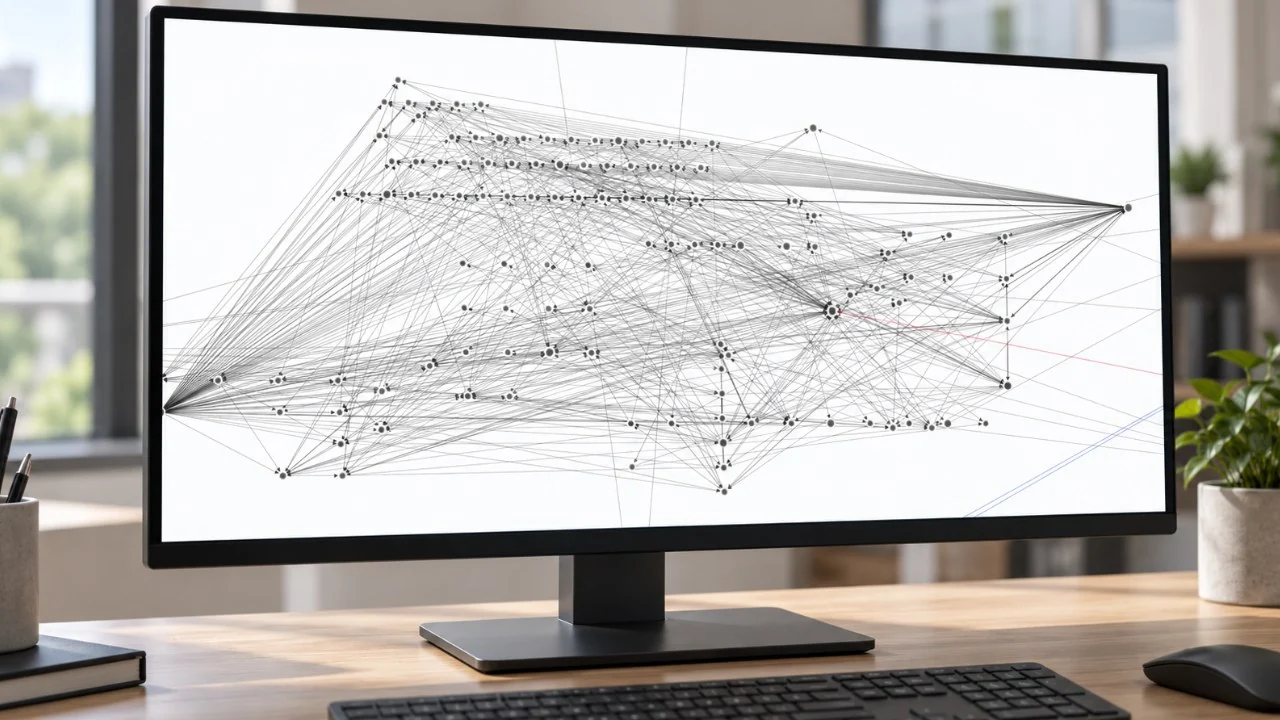
Thousands of transactions in a short period suggested automation intended to obscure the trail.
Investigators tracked repeated transfers among addresses, including returns to wallets used earlier in the sequence. Many addresses first received exactly 1 TRX, Tron’s native token used to pay transaction fees, before accepting more funds and forwarding assets elsewhere. Chainalysis added: “This repeated sequence suggests a programmatic process for moving and redistributing the stolen funds.”
Investigators Trace Access and a North Korea Connection
Binance co-CEO Richard Teng disclosed additional breach points and bypassed approval controls, alongside a self-destruct mechanism that destroyed tools and traces. Chainalysis traced outflows to about 4:20 p.m. Eastern time on Oct. 29 and identified an Ethereum wallet funded through Tornado Cash, a crypto mixer that obscures links between deposits and withdrawals. That wallet submitted valid signed authorizations, or cryptographically signed permissions, enabling a Binance hot wallet to run attacker-deployed software and transfer assets into attacker-controlled addresses.
Laundering patterns initially suggested involvement by Tradertraitor, a North Korean cybercrime group. Chainalysis then observed stolen Binance assets mixing with proceeds from September’s Bitget theft, previously attributed to North Korean actors, strengthening its attribution of the hack to Tradertraitor. Separately, TRM Labs attributed the Binance attack to Tradertraitor with high confidence, citing onchain and offchain intelligence.
Stablecoin Swaps Race Against Asset Freezes
Chainalysis explained:
“Freezing funds takes time. The attacker attempted to stay ahead of that process by quickly moving $500 million of stablecoins into a wallet whose job it was to swap out those freezable assets to non-freezable assets.”
Such stablecoin freeze and blacklist controls can prevent designated addresses from transferring affected tokens, while native ether has no equivalent issuer-controlled mechanism.
Over nearly 20 minutes, the wallet exchanged $325 million in stablecoins for approximately $285 million in ether, then moved the remaining $175 million to intermediary wallets 10 minutes later. Freezes began by 5:14 p.m. Eastern time on Oct. 29, with Chainalysis reporting about $2.8 billion frozen in its Oct. 30 account. Binance separately put the total at approximately $3 billion that day.
The exchange also said it had reserved more than $6.34 billion in company funds to cover the incident, excluding frozen assets. Of that amount, $5 billion was already held in affected tokens. Purchases through market and over-the-counter channels were underway to match the remaining assets.