Baiting in cybersecurity is an attack that tempts a person into doing something unsafe, such as plugging in a USB drive, opening a fake file, or claiming a “free” download. It works because curiosity, urgency, and reward can beat caution. Verizon’s 2024 Data Breach Investigations Report found that 68% of breaches involved a non-malicious human element, which shows why baiting still causes real damage [source: Verizon].
TLDR: Baiting tricks people with something tempting, like a lost USB labeled Payroll 2025 or a fake gift card link. USB baiting targets devices, while social engineering baiting targets human trust. For example, if an attacker drops 20 infected USB drives in a parking lot and only 4 employees plug them in, that is still enough to infect workstations or steal login data. Prevention needs training, device controls, email filters, and a clear rule: unknown media and surprise offers must be treated as hostile.
What Is Baiting?
Baiting is a form of cyber trickery where the attacker offers a lure. The lure may be physical or digital. The goal is simple: make the victim take the first step.
That step could be:
- Plugging in an unknown USB drive
- Opening a file from a stranger
- Clicking a fake prize link
- Downloading “free” cracked software
- Scanning a malicious QR code
The attack does not always need advanced hacking. Often, it only needs a believable excuse. Honestly, it feels ridiculous that a cheap USB stick can still bypass costly software controls, but it happens when people are rushed or curious.
USB Baiting Attacks
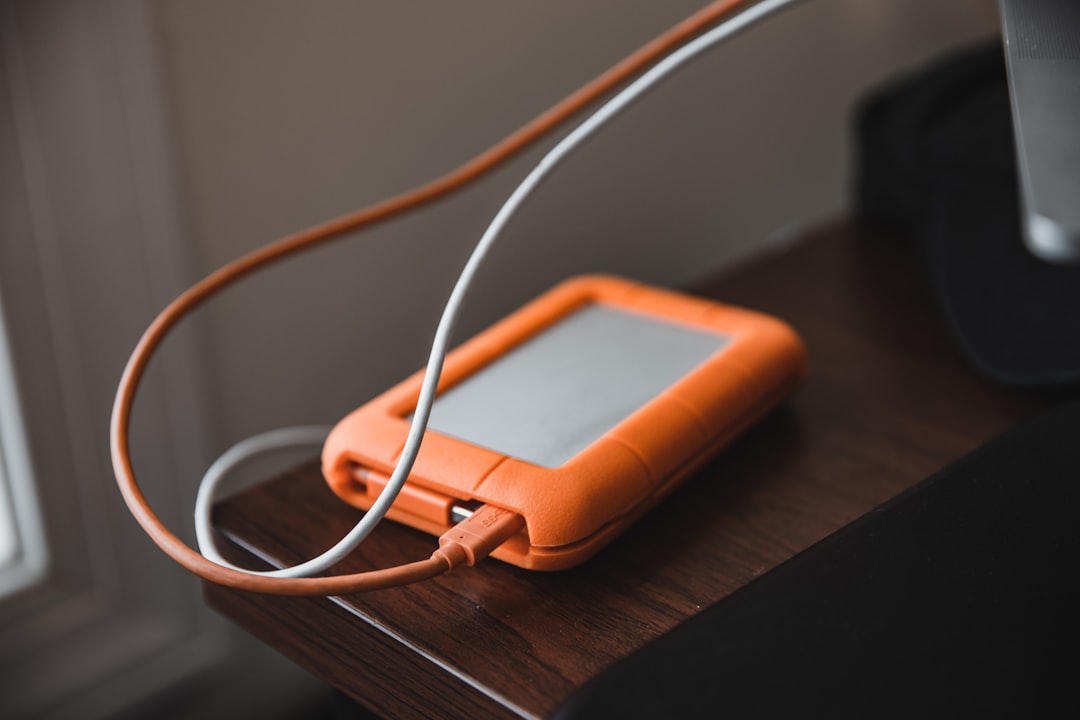
USB baiting uses removable media as the trap. An attacker leaves infected USB drives in places where staff may find them. Common spots include parking lots, reception areas, cafes, elevators, and conference rooms.
The device may have a label such as Confidential, Bonuses, Client List, or HR Files. That label is not random. It is meant to create curiosity or panic.
Once plugged in, the USB may:
- Install malware
- Open a fake login page
- Run commands without clear warning
- Copy files from the machine
- Act like a keyboard and type commands fast
Some attacks use simple storage devices. Others use hardware that pretends to be a keyboard. That is why blocking file access alone may not be enough.
Social Engineering Baiting
Social engineering baiting uses emotions instead of hardware. The attacker may promise a reward, secret information, free access, or urgent help. The victim clicks because the offer feels useful or time sensitive.
Examples include:
- A fake email offering a company bonus form
- A message claiming a package is waiting
- A fake download for paid software
- A social media post offering free event tickets
- A QR code near a parking meter that leads to a fake payment page
The catch is that people often know the rule, then break it when the bait looks personal. A fake email that takes 12 seconds to read can still beat years of security reminders if it lands during a busy morning.
USB Attacks vs Social Engineering
Both attacks use temptation. The difference is the delivery method.
| Attack Type | Main Bait | Main Risk |
|---|---|---|
| USB baiting | Found device or free storage | Malware, data theft, device takeover |
| Social engineering baiting | Prize, file, link, message, QR code | Credential theft, fraud, malware download |
USB attacks often need physical access near the target. Social engineering can reach thousands of people at once through email, chat, ads, or social media. Both can hurt a business fast.
How Organizations Can Prevent Baiting
Prevention works best when people and systems support each other. Training alone is weak if devices accept anything. Technical controls alone are weak if users can approve risky prompts without help.
Strong controls include:
- Block unknown USB devices by default.
- Disable autorun on all workstations.
- Use device control software to allow only approved hardware.
- Filter email and web traffic for known scams and malicious links.
- Run phishing and baiting simulations with short feedback.
- Teach staff to report found devices instead of testing them.
- Use multi-factor authentication to reduce damage from stolen passwords.
- Separate admin accounts from daily work accounts.
Clear policy also matters. Employees should know who to call, what to hand over, and what not to touch. If reporting feels slow or awkward, people may try to “check quickly” on their own. That is where trouble starts.
What Individuals Should Do
A person should never plug in a found USB drive. Not at home. Not at work. Not “just to see what is on it.” The safe move is to give it to IT or dispose of it through approved channels.
For digital bait, the same rule applies. If an offer looks too useful, too urgent, or too generous, it needs a second check. The user should visit the official site directly, not through the link in the message.
FAQ
What is baiting in cybersecurity?
Baiting is a cyberattack that tricks a person with a tempting offer or object. The goal is to make them click, download, log in, or plug in a device.
Is USB baiting still common?
Yes. It still works because people are curious. A labeled USB drive can create enough interest for someone to ignore normal rules.
How is baiting different from phishing?
Phishing usually uses fake messages to steal data. Baiting may use messages too, but it focuses on a lure, such as a free download, prize, or physical device.
What should employees do with a found USB drive?
They should not plug it in. They should report it to IT, security, or a manager and follow the company’s device handling process.
What is the best way to stop baiting attacks?
The best defense is a mix of user training, USB restrictions, email filtering, web protection, and multi-factor authentication. No single control is enough.