Did you simply hear about WordPress documents permissions and are questioning if yours are set correctly? Or are obtaining an error that you don’t have the best consents? Either way, this is the right blog post for you.
File permissions are an extremely integral part of safeguarding your internet site They keep your website secured down while providing WordPress itself, its plugins, and other scripts the capacity to customize what they require to.
Yet often points can go wrong. Errors may pop up, or data consents obtain changed to improper worths. Because situation, it’s useful to know exactly how WordPress documents permissions work and just how to utilize them.
That’s precisely what we’ll describe today. Below, you’ll find out all you need to understand about file approvals, exactly how change them, and finest practices to maintain your website working smoothly.
Recognizing Data Approval Levels
If you wish to discover how to change data authorizations in WordPress, you’ll require to comprehend the basics initially. For that, we need to check out Linux permissions. Below’s a quick crash course on that particular topic.
Sorts Of File Permissions
There are 3 major sorts of permissions files can have. You can establish these not just for private documents, but whole directories/folders.
- Read (r) — This allows a customer to view a documents’s contents or the names of documents within a directory site.
- Write (w) — Write authorization enables an individual to modify the data’s web content. They may likewise create, erase, or rename files within a directory site.
- Execute (x) — Below, individuals might implement programs and scripts, or accessibility a directory site’s documents and subdirectories.
Permission Teams
Nevertheless, that precisely can have these authorizations? In Linux, there are three groups of individuals who can access a file/directory.
- User (u) — Describes the proprietor (typically the creator) of the file/directory.
- Group (g) — Several users that share usual consent degrees. Any customer can be in one or more groups.
- Others, World, or Public (o) — Any type of users who are not the owner of the data and are not in a defined group.
For every of these, you can establish various degrees of approval. In WordPress, these are called individual roles For example, you wouldn’t desire random website subscriber to have the very same approvals as the manager. That would certainly be a recipe for disaster.
Symbolic and Numeric Symbols
When you deal with file consents, they are stood for either in symbolic or numerical symbols.
Symbolic symbols utilizes the letters over to denote read (r), compose (w), and execute (x) approval, or a dash for none. They are organized in 3 trines with the very first three letters describing Individual (u) approvals, the next three to Team (g) consents, and the final three to Others authorizations (o).
Take this instance: rwxr-xr--
Right here, the User has complete consents (rwx), the Group has read and carry out approval (r-x), and the Others group has just read permission (r–).
With numeric symbols, each approval is instead assigned a worth:
- Read (r) = 4
- Create (w) = 2
- Perform (x) = 1
These are totaled to form a three-digit number standing for approvals for Individual, Group, and Others.
Making use of the same example above, the Individual’s permission is 7 (r + w + x), the Team’s 5 (r + x), and Others’ 4 (r). That means, the same consent degree’s numerical notation is 754
Submit Permissions in WordPress
In the context of WordPress and internet sites in general, file authorizations utilize the exact same concepts as above. However there are likewise a few differences you’ll intend to recognize.
- File ownership — In a WordPress atmosphere, data and directories are frequently had by the web server procedure ( www-data for Apache and nginx for NGINX) rather than private users.
- Plugin and theme factors to consider — WordPress plugins may need read and create access to particular data and directories to operate effectively. Plugins generally utilize the Filesystem API to user interface safely with your server.
- Some groups are currently built in — As pointed out, WordPress uses integrated roles like Manager, Editor, and Factor. Contributors only have the capacity to produce and edit their very own write-ups, not others. Functionally, this means they have actually reviewed approval on all post/page files, and read/write approval on post/page documents they develop.
- Keep an eye out for shared organizing environments — Shared holding can offer problems with file approvals. Particular data may be secured down to prevent other users on your multi-website web server from accessing delicate data. You might locate some files set to read-only also for administrators, needing root access to modify.
The Dangers of Incorrect Data Permissions
Currently comes the concern, why is this even essential? Why should you respect this really technical-sounding subject?
The reason is that documents approvals develop the foundation of website security. Being too loosened with them can seriously jeopardize your website in the following ways:
- Hacking and malware — Improper permissions can let cyberpunks slip with and do basically whatever they desire. That consists of installing malware, checking out exclusive documents, or erasing your site.
- Site takeover — If someone handles to get into your internet site thanks to lax authorizations, they might quickly take ownership of your account and lock you out of your very own web site.
- Information leakage — Incorrect permissions can lead to visitors gaining access to private documents, consisting of photos, unfinished/test/draft web pages, and private data.
- Inappropriate data accessibility — Certain consents may enable individuals to alter existing files on your internet site, or upload and carry out destructive files like malware scripts.
Yet it’s not just about too much gain access to, it can also be too little. Making your consents also limiting will undoubtedly break your website by protecting against WordPress from working appropriately. It’s a fine line in between excessive and inadequate with data consents.
WordPress Documents Approval Best Practices
Prior to you start combing with your internet site data trying to find anything out of place, it is necessary to recognize what an excellent practices for documents authorizations resemble WordPress. So, let’s review that now.
Don’t Adjustment Permissions Unless Required
The very first thing that is essential to keep in mind is that, most of the times, you won’t need to change file consents. If you are using a great holding company and install WordPress appropriately, this component of your site ought to be set up in the correct method automatically.
So, unless you’re encountering a particular WordPress error , don’t touch your file permissions, particularly if you don’t understand what you’re doing. Tinkering settings you don’t understand can trigger more harm than good.
Some web hosts, particularly shared hosts, may make some consents more limiting because of the nature of the hosting. If you’re having a problem with insufficient authorizations, it may be best to call your host and ask for assistance.
Suggested Consent Levels
If you do encounter an issue and you’re not exactly sure what permission settings your data and directory sites ought to get on, there is info for that in the official WordPress documentation
Below is a fast rundown of generally suggested approvals for various files and folders. Nonetheless, remember that this varies depending upon your configuration.
- Directories — 755 (rwer-er-e). For your server to work properly, most directories need carry out permissions.
- Data +. htaccess — 644 (rw-r– r–). This allows individuals to see public documents on your website without being able to edit them. The majority of documents ought to only be writable by your individual account.
- wp-config. php — Differs; 400 (r——), 440 (r– r—-), 600 (rw—–), or 640 (rw-r—-) might be appropriate relying on site setup and protection demands. The most vital action is to prevent arbitrary visitors from accessing this important file.
Do not Be Also Restrictive
Locating the right equilibrium with file consents can be demanding, however you can’t simply set them all to”000 While your site would be really protected, at the very same time, nobody would certainly have the ability to use it.
Features on your site, from your web server to plugins to WordPress itself, normally require some access to specific documents and directories to proceed functioning effectively. Even visitors, who must not be offered compose or carry out accessibility to a majority of data, require to a minimum of have the ability to “read” the public-facing components of your website.
It can be tempting to secure down on file approvals, but you can do some significant damages. When plugins and features quit working, a plethora of cautions will appear on your dashboard. You could also cause your internet site to run into the feared White Display of Death if you’ve severed WordPress’ access to core documents.
Utilize the Principle of Least Benefit
The principle of least benefit states that customers (including your web server and WordPress itself) should be given equally as much access as what’s needed to do their jobs.
Granting “root” ownership implies providing full control and accessibility to the whole system, which is normally too much. If a hacker get to a WordPress site with root benefits, they can possibly wreak havoc on the entire server.
Rather, the owner of most documents must generally be your web server customer, normally nginx (NGINX) or www-data (Apache), both of which only have the approvals required to function properly. This restricts the damages bad actors can create.
There are some scenarios where origin possession is necessary, so you shouldn’t go altering permissions if you don’t recognize what you’re doing. At the very same time, seeing it can be a cause for problem– particularly if you notice that a data or directory site owner has actually instantly changed.
In any various other scenario where you might be developing documents or assigning owners, follow the principle of the very least opportunity. Do not hand out extreme read, compose, or execute approvals. A lot of files you develop on your web server will certainly not require root possession.
Back Up Your Site
Prior to you touch any type of sensitive settings on your web site, it’s finest method to back up both your internet site and data source data
Things can easily go wrong when modifying file consents, so this gives a safeguard. If you mistakenly break something on your web site, you can simply roll back your server
Never ever Utilize 777
Setting any kind of documents or directory site approvals to 777 is generally offering every person in the world complimentary reign over your site.
This gives any random visitor the capacity to watch data, modify and erase them, upload potentially harmful programs, and execute scripts. Clearly, this is a horrible concept.
While it might seem benign to offer complete consents to just one data, a savvy cyberpunk can conveniently utilize this to implement a harmful script or escalate their advantages and worm their method deeper right into your server. So simply don’t do it.
Exactly How to Modification WordPress Data Permissions
Now that we have actually covered the very best techniques for data consents, let’s find out how to alter these in different web server configurations.
cPanel or Dashboard
Most web hosts use accessibility to cPanel or some customized dashboard You’ll wish to inspect your organizing supplier’s documents, but within cPanel you can generally most likely to the Submit Manager , then appropriate click any type of folder or data and click Modification Permissions

FTP/SFTP
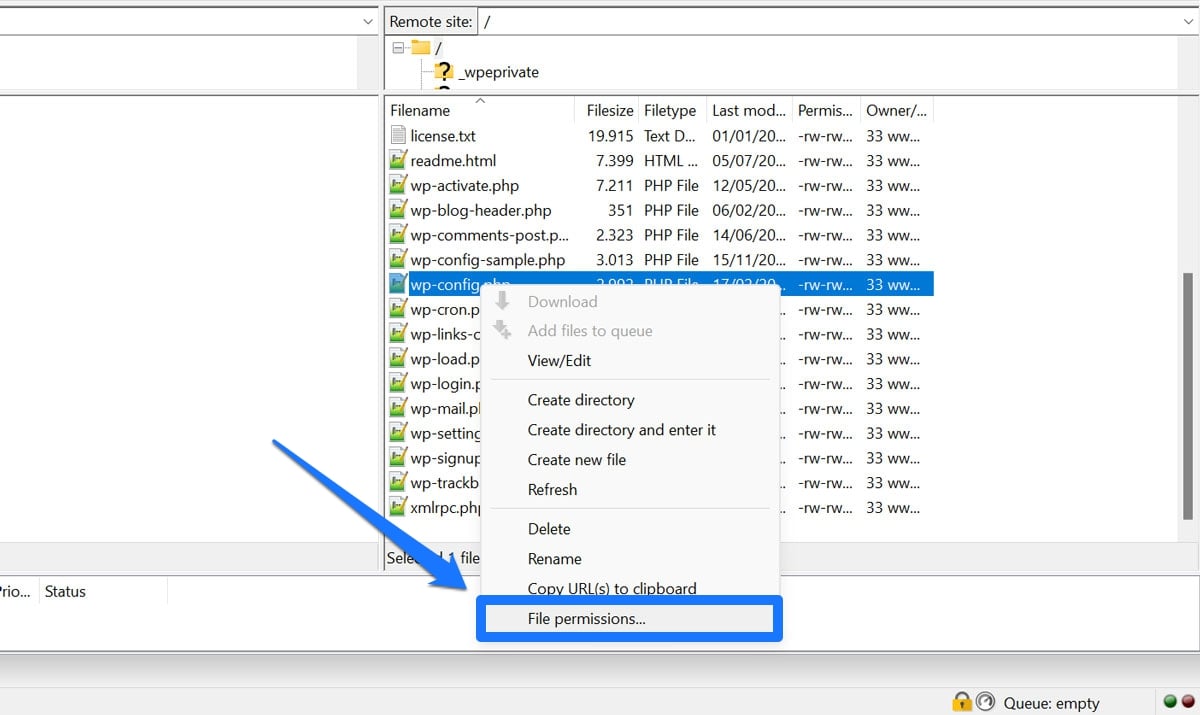
You can additionally transform permissions using FTP/SFTP access. Beginning by mounting an FTP customer like FileZilla and log in to your web server. Right click any file or folder and choose Submit consents …
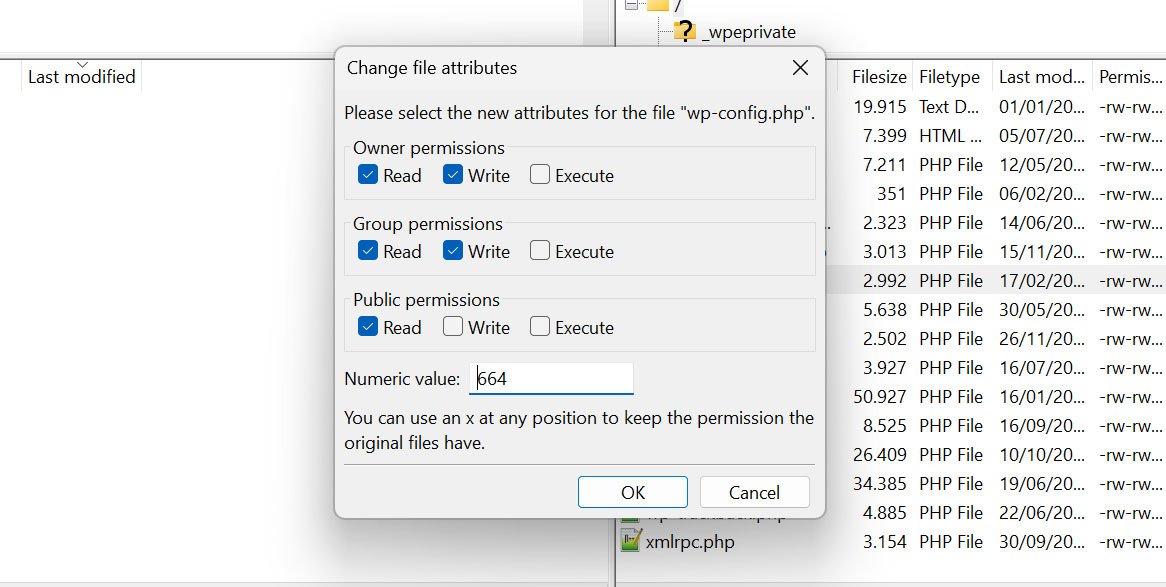
After that, go into the numeric worth or just tick packages you want to establish.
SSH/Command Line
For this action, make use of a command line access tool. This is generally given by your web host. You’ll wish to utilize the cd command to navigate to the directory of whatever documents or subdirectory you desire to transform. For example:
cd public_html/ example_folder
You can then customize the approvals of a file or subdirectory in this folder making use of the chmod command.
chmod 755 example.html
You can additionally recursively set approvals for a whole directory site at the same time, however be careful when doing this.
chmod -R 755 example_subfolder
Make use of a Plugin
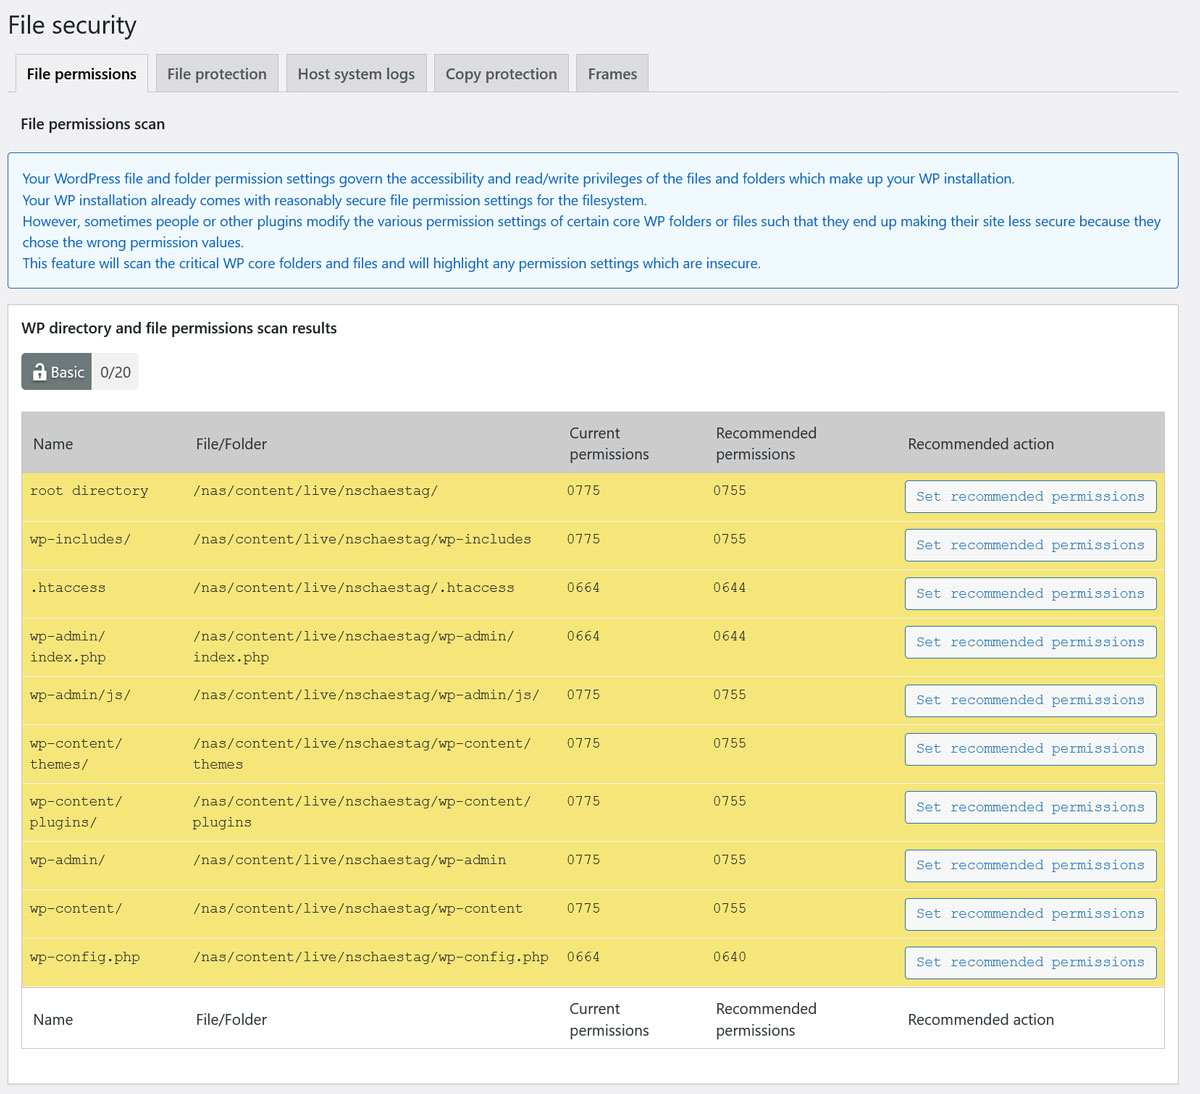
Some safety and security plugins will enable you to quickly switch data permissions from the control panel. One instance is All-In-One Safety (AIOS) With this, you can alter file consents, identify troubled file permissions, and solution problems in one click.
Common Documents Approval Mistakes in WordPress
Finally, allow’s take a look at a couple of common file permission mistakes in WordPress and what triggers them.
- 403 Not allowed (You don’t have consent to accessibility on this server) — You’ll see this error if you try to access a file when you do not have check out authorization. For example, visitors will experience this if they attempt to gain access to unpublished write-ups or web pages. You may want to examine your consents if you’re seeing this as the administrator.
- Required data permissions missing out on — Specific plugins might throw up this mistake. This might be created if your internet site data are not owned by nginx or www-data
- You need to make this file writable prior to you can conserve your modifications — You’ll see this in the WordPress editor if you lack create access to particular data.
- Approval rejected. Mistake code: 3 — This mistake appears when trying to modify or upload data to your site. The reasons differ, consisting of internet site files being owned by origin as opposed to nginx or www-data , needing origin gain access to, or just doing not have read/write authorizations.
- Setup stopped working: Might not develop directory site — If you see this when installing or updating themes and plugins, it suggests that WordPress does not have compose authorization to the directory it’s trying to use.
Proceed With Caution When Changing WordPress Documents Permissions
File consents are an extremely fundamental part of keeping web site protection, so you shouldn’t alter them gently. One little tweak could break your web site, or let hackers much more conveniently slide via.
But it’s good to understand just how these approvals function, particularly if errors start surfacing. Now you understand what to do– and especially what not to do– if ever you require to alter your WordPress file consents.
Did you handle to take care of a WordPress file permission error? Share your experience in the remarks and aid others with the exact same issue!