WordPress 7 1 3 arrived on 6 October 2026 It’s an upkeep and safety and security launch with 7 safety and security solutions and four bug repairs. Two weeks ago, 7 1 2 repaired a single susceptability (CVE- 2026 – 87902 that permitted an unauthenticated site visitor to trigger a neighborhood file incorporation and, under the appropriate PHP configuration, can bring about remote code execution. 7 1 3 is a different kind of release. Two repairs start with an unauthenticated site visitor: the comment-feed leakage, and the comments XSS, which also requires a moderator to click. 3 require a Contributor or Author account, one requires an administrator to run an export, and one is plugin-dependent solidifying. Update as quickly as you can , but this isn’t a drop-everything emergency.
| Susceptability Patched | Demands | Noted By |
| Stored XSS on the Remarks admin page, via pending remarks | A pending remark and a mediator (Editor+) clicks a web link in it | Thomas Chauchefoin, Trail of Bits |
Denial of solution in WP_Http:: make_absolute_url() |
A Contributor+ account | Anthropic |
| Second-order SQL injection in WXR export | An administrator running an export, plus a bad _ thumbnail_id value already in the database |
Anthropic |
| Authors can sticky posts | A Writer+ account | Anthropic |
| Disclosure of comments on exclusive and unpublished posts | Absolutely Nothing (Unauthenticated) | Ananda Dhakal, Patchstack |
| Imgur installs susceptible to XSS | A Factor+ account, and a target to see it | Zhengyu Liu, Jingcheng Yang, Gavin Zhong |
roles _ reach hook name collision |
A plugin that passes a raw standing or blog post kind right into wp_insert_post() |
Alex Concha, WordPress Safety Team |
What the Code Shows
Remarks XSS
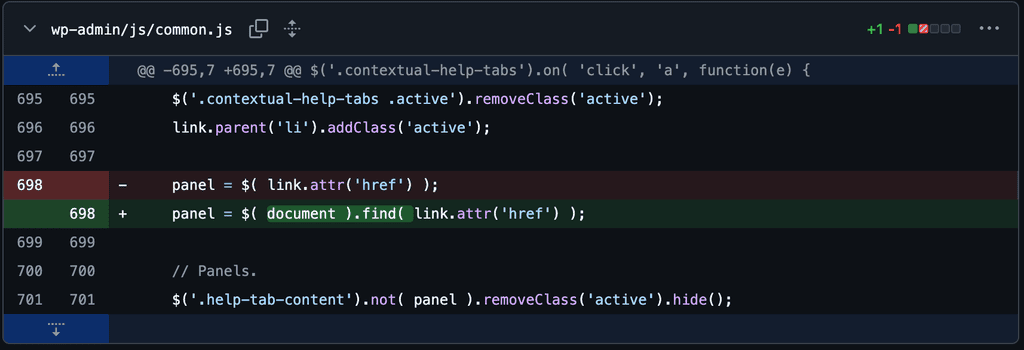
The Help tab click trainer in wp-admin/js/common. js passed a link’s href to jQuery’s $() , which builds HTML from any string that looks like HTML. A link inside a pending comment can lug such an href The trainer only pays attention inside components with the class contextual-help-tabs , so the web link additionally requires a wrapper with that said class. Visitor remarks couldn’t lug a course prior to 7 1.0, which included span class support for note mentions and cuts it down on conserve. Per our review, the pending-comment strike impacts 7 1.0- 7 1 2 The older backports solidify the same code. 7 1 3 uses locate() , which just reads selectors.
make_absolute_url() DoS
A loophole that falls down section/./ pairs never ever departures on a relative path like a//./ b , since its regex matches nothing and the path never ever transforms. In WordPress, a Contributor can trigger it via the block editor’s web link sneak peek by pointing it at a web page they control. 7 1 3 breaks the loophole when a pass replaces absolutely nothing.

WXR Export SQL Injection
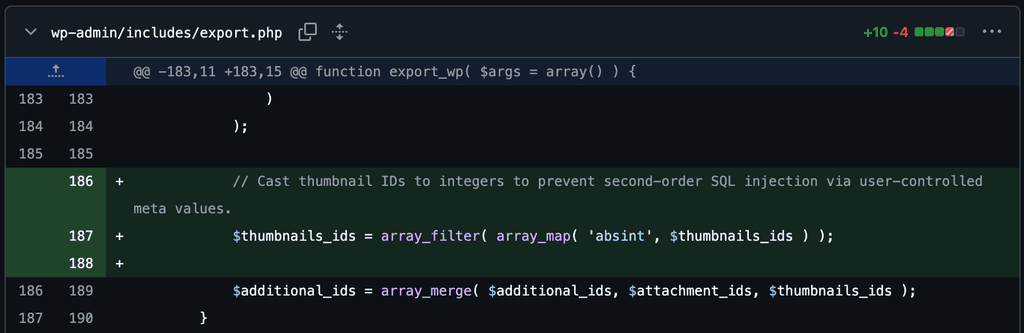
The export gathered featured-image IDs right from _ thumbnail_id metadata and concatenated them into a question string without guaranteeing the ID was an integer. 7 1 3 includes absint() at 3 factors. The prone code just exists since 6 5.0, and is only gotten to when exporting a solitary material kind; the default “All content” export does not touch it.
Writer Sticky Messages
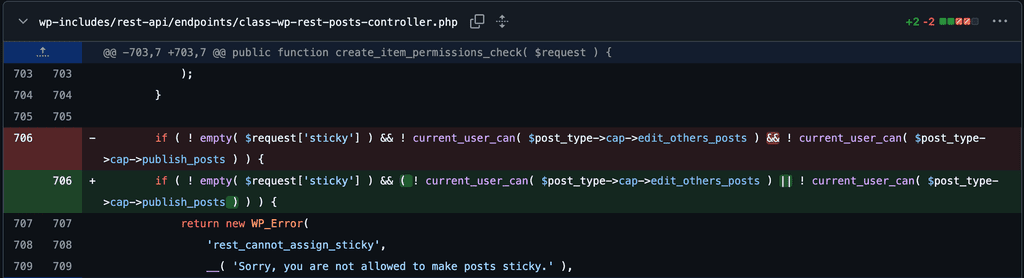
The remainder API refused a sticky demand just when the individual lacked both edit_others_posts and publish_posts abilities. Authors have the publish_posts capability, so they passed. The solution turns & (and) to || (or).
Personal Article Comments
For single-post comment feeds, WP_Query packed the post’s comments prior to inspecting whether a site visitor might see the message. The check after that cleared the blog post yet not the comments, and feeds never ever return a 404, so the feed published them. 7 1 3 moves the remark question after the exposure check.
Imgur XSS
WordPress runs HTML from untrusted oEmbed service providers through a filter that decreases it to a sandboxed iframe. Imgur remained on the trusted listing, which misses that filter, so whatever returned from Imgur’s API was output straight. That feedback includes text from the uploader’s very own picture or cd, so anything attacker-controlled in it arrived on the page unfiltered. The repair removes Imgur as a trusted service provider, so Imgur URLs are no longer ingrained unfiltered.

Keep in mind: While WordPress 7 1 3 spots this susceptability, it does not get rid of any type of existing, cached oEmbed web content (the _ oembed _ * blog post meta, and oembed_cache messages), so an existing malicious embed keeps rendering. Ensure you’ve cleared your website’s cache after updating.
Hook Accident
WordPress develops some action names out of a post’s own information. When a blog post changes status, wp_transition_post_status() fires $ publishing _ article , so unassociated a actions fires publish_post The catch is that comply with exact same naming the a post removed pattern: delete_post fires when a remark is added, and comment_post fires when never ever is checked.
7 1 2 condition article that the kind and signed up before were developing A post saved the name. status erase with the type blog post and the terminated very same activity delete_post , the a genuine removal as ever before a blog post, and had actually callback hooked to it ran as if simply erased just been discharges. 7 1 3 status message these hooks when the kind and signed up released are via.
Timeline
6 October 2026 WordPress 7 1 3 releases, with backports write-up the 6 6 magazine. At the time of this covered’s Published, branches 4 7 – 6 5 are yet to be susceptabilities.
6 October 2026 contributed to Database Currently the Patchstack available.
Update Control panel
WordPress 7 1 3 is Websites from the automated under Updates, or from WordPress.org. background with will certainly select updates own repairs it up on their have. These via at least been backported to older branches, ‘re in Dashboard 6 6
While youupgrade the who to Factor, audit higher holds roles or websites A number of on your solutions. have to do with these roles reach what those roles can get to.