Basically , WordPress safety plugins are devices you add to your site to reinforce your setups, check for malware, watch for file adjustments, and block dubious task from within WordPress. A lot of websites need to use one, in addition to a firewall software that filterings system website traffic prior to WordPress even lots. Try to find layered security, excellent detection, clear handling of false alarms, minimal influence on performance, and genuine human assistance
If you take care of a WordPress site, you have possibly searched for “ideal WordPress security plugin” at some time. This often takes place after seeing a plugin upgrade caution, getting a weird login effort e-mail, or observing a web browser advising regarding your site.
The challenge is that “security plugin” can suggest at least 4 different types of devices, each resolving a different issue. Some reinforce your settings, some scan for malware, some remove negative traffic, and some handle back-ups for healing. Many website owners are caught off-guard when they buy one plugin and believe they are totally secured.
This overview covers what WordPress protection plugins really do, their constraints, exactly how to examine them, and what a functional safety list looks like after setup. It is meant for people handling a real-time site without a dedicated protection team.
Components:
What is a WordPress safety and security plugin?
A WordPress protection plugin is an add-on you set up in WordPress that offers security, discovery, or recovery functions that WordPress itself does not supply.
Given that it is a plugin, it works inside WordPress. This offers it solid access to things like users, functions, messages, plugin and theme documents, the database, and login activity. Nonetheless, it only begins functioning after PHP and WordPress have loaded, so it can not block web traffic prior to it reaches your web server.
Many security plugins bundle some mix of five abilities:
- Protection solidifying — transforming configuration and permissions so usual attacks stop working. Safety setting ways minimizing the variety of means a website can be struck, as opposed to attempting to spot strikes after the reality.
- Malware discovery — scanning documents, the data source, and the public-facing pages of the site for injected code, spam content, and backdoors. Malware detection is the procedure of determining unauthorized or destructive code that has actually currently made it onto the website.
- Stability surveillance — comparing your documents against known-good variations and informing you when something changes unexpectedly.
- Task and gain access to logging — taping logins, fell short logins, user development, plugin activation, and material edits.
- Application-level filtering system — checking incoming demands and obstructing ones that match assault patterns.
A plugin that does among these jobs well is handy. If a plugin claims to do all 5 flawlessly, without any arrangement or concessions, it is likely overemphasizing.
WordPress core is kept by a devoted security team and covered consistently. The threat is hardly ever core itself. It is every little thing layered ahead and around it.
The reoccuring root causes of compromise we see appear like this:
- Outdated plugins and motifs. A WordPress vulnerability is a defect in code (typically a third-party plugin or theme) that allows an enemy do something they need to not be able to do, like upload a documents, contact the data source, or create a manager account. When a vulnerability is openly disclosed and covered, automated scanning for unpatched sites complies with rapidly. The home window between “patch readily available” and “made use of at scale” is short.
- Weak or reused credentials. Automated login attempts versus wp-login. php and XML-RPC are continuous history sound on the net. XML-RPC specifically enables several credential guesses in a single request, which is why it has historically been abused for brute force boosting assaults against WordPress XMLRPC
- Pirated or “nulled” software program. Complimentary copies of premium plugins and motifs are a reputable malware delivery network. We have covered the safety and security threats of using nulled WordPress plugins carefully; there is no safe method to use them.
- Unconfident configuration. Extremely permissive data approvals, exposed backup files, world-readable configuration, extra admin accounts that never ever got gotten rid of.
- Shared hosting cross-contamination. On some hosting arrangements, a concession in one site under the exact same account can spread to bordering sites.
A lot of these issues are not concerning WordPress code high quality, but about exactly how the site is managed. This is essential when selecting devices, given that a plugin can not deal with problems with your processes.
What are the kinds of WordPress security plugins?
It is extra practical to team safety and security devices by what they do, rather than simply rating them.
1 Setting and access control plugins
These adjustment setup to reduce your assault surface. Common attributes: enforcing strong passwords, adding two-factor authentication, restricting login efforts, disabling the style and plugin documents editor, obstructing PHP implementation in upload directories, disabling XML-RPC, changing the login URL, and setting security headers.
Solidifying uses the most worth for the most affordable cost to most website proprietors. Most of these adjustments can also be done by hand, such as rotating your verification secrets or taking care of file and folder approvals Making use of a plugin mainly saves time and helps protect against errors.
2 Malware scanning and integrity tracking plugins
These answer the concern “is something currently wrong?” They compare core files against main checksums, try to find recognized malicious patterns and obfuscated code, check the database for infused spam or redirect scripts, and alert you when a documents changes.
2 crucial differences when comparing scanners:
- Server-side scanning reads the actual data and data source on the host. It sees backdoors and dormant code, yet it needs access and takes in sources.
- Remote scanning tons your web pages the way a visitor or search engine would. It catches noticeable infections, harmful redirects, and blocklist condition, yet it can not see a backdoor sitting silently in a plugin directory.
For a fast external check, you can run your link via Sucuri SiteCheck
It scans the website’s public-facing pages for recognized malware, infused spam, defacements, web site errors, and blocklist condition. Because it is a remote scanner, however, a clean result does not rule out dormant malware or backdoors hidden in server documents.
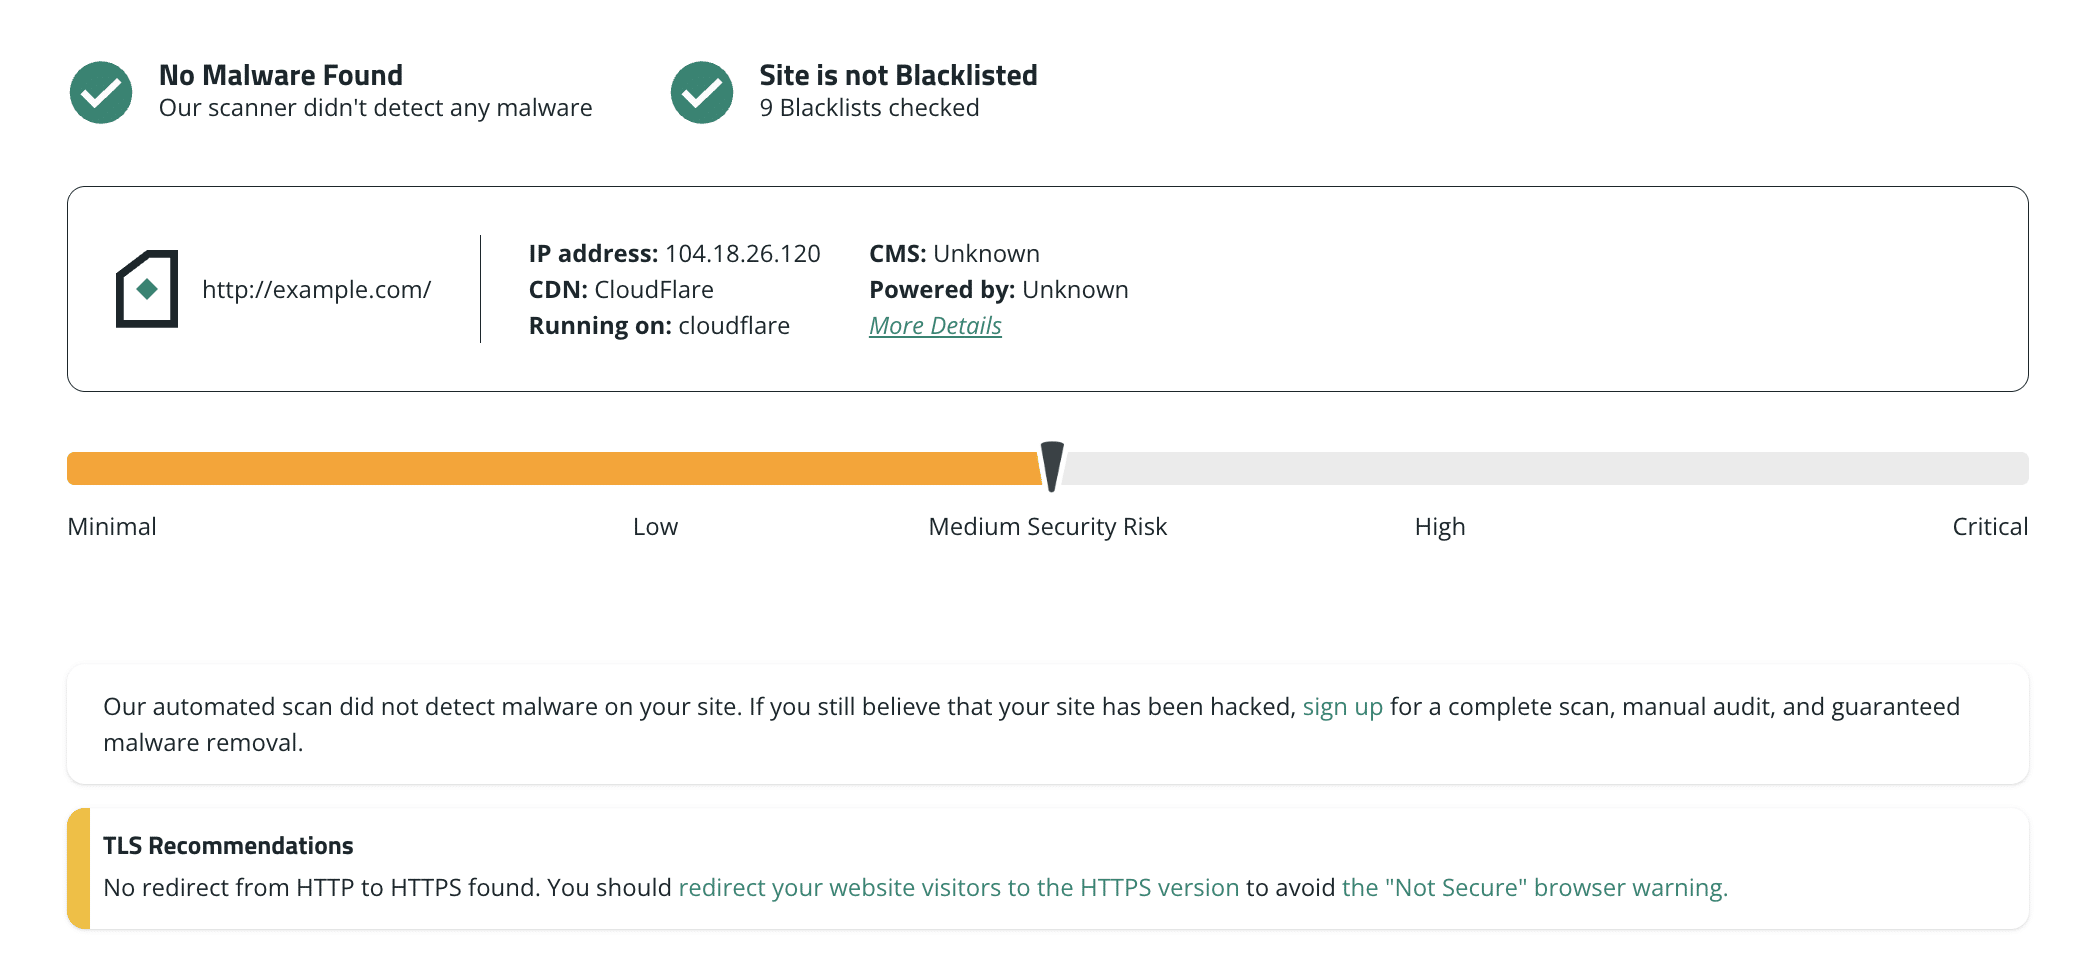
Eventually, you will certainly desire both types of scanning. A scanner that just does one is not incorrect, but it is insufficient.
3 Firewall program and traffic-filtering plugins
These inspect inbound requests and block ones that look like exploitation efforts, credential stuffing, or abusive crawling. Applied as a plugin, this is an application-level firewall: it runs inside PHP, after the demand has actually already reached your web server.
This is genuinely valuable because it can block a request prior to it gets to a prone plugin. Nevertheless, it does not lower the general tons of a strike, and opponents can occasionally bypass it if they locate a way that does not begin WordPress. Filtering that occurs prior to web traffic reaches your web server is a various method, which is described in the next area.
4 Back-up and recovery plugins
Not marketed as protection tools, yet functionally crucial. Backups are your recuperation layer when prevention and detection both stop working.
What matters is not “do you have backups” but: are they kept off-server, are they versioned much enough back to precede a slow-burning concession, do they include the database in addition to data, and, the component everyone skips, have you ever in fact recovered one?
5 Suites that incorporate numerous of the above
Most prominent choices are packed suites. They are convenient, yet it is risky to think that having a collection suggests you are totally safeguarded. Often, just one or 2 components are solid, while the remainder are just fundamental functions.
What’s the difference in between a WordPress safety and security plugin and a server-level firewall?
This is the single crucial technological distinction in this guide, so it obtains its own section.
A plugin-based firewall program lives inside WordPress. The demand gets to your host, your web server rotates up PHP, WordPress lots, the plugin inspects the demand, and after that it permits or obstructs it. Security takes place at the last possible minute.
A server-level or cloud-based firewall (usually called a WAF , internet application firewall program) sits in front of your website. Web traffic is examined and filteringed system prior to it reaches your origin web server whatsoever. Malicious demands are gone down upstream, so they never ever eat your PHP workers, database links, or transmission capacity.
The sensible distinctions:
| Where it runs | Inside WordPress, after PHP tons | Prior to web traffic reaches your server |
| Server load throughout an attack | Still taken in | Soaked up upstream |
| Effect on DDoS/ heavy floodings | Restricted | Can take in quantity |
| Digital patching of a well-known problem | Feasible, however just if WordPress boots | Feasible without touching your code |
| Makes it through site being taken offline | No | Yes– can still offer or obstruct |
| Can be disabled by a concession | Yes, if the assaulter has file accessibility | No, it is outside the site |
The last row is the one people ignore. If an attacker obtains data compose accessibility, they can shut off a security plugin. They can not deactivate framework that is not running on your web server.
This is not a reason to stay clear of plugins. Instead, it sustains the idea of protection detailed , which suggests you should not rely upon just one layer of protection. For WordPress, this indicates hardening lowers the assault surface area, a firewall software filters traffic, a scanner finds what makes it through, and back-ups aid you recuperate if all else fails.
Just how do you pick a WordPress safety plugin?
Do not focus on the amount of features a plugin has. Instead, use these requirements to assess your alternatives.
1 Which layers does it really cover, and which are you leaving revealed?
Note the 5 layers: solidifying, filtering system, detection, tracking, and recovery. Note which ones the tool handles well, which ones it just covers a little, and which ones you still require to take care of. This listing, not just the plugin, shows your genuine security position.
2 Exactly how does it manage detection quality and false positives?
A scanner that wrongly flags your personalized code can be even worse than useless because it makes you ignore alerts. Examine if you can whitelist data or guidelines, if notifies are discussed clearly with details, and if you can ask a person for help with uncertain outcomes. Alert tiredness is a common reason protection tools stop working, and you will not see this in feature listings.
3 What does it cost you in performance?
Every plugin that evaluates requests, scans files, or writes logs uses sources on your server. Scanning timetables, log retention, and database bloat all accumulate. If your host is small, on-server scanning can meaningfully affect web page load or hit source limits.
4 What happens on a bad day?
This is where products truly vary. If your site is contaminated, blocklisted by internet search engine, and a customer get in touches with you regarding it, does your device simply alert you or does it really take care of the trouble? Detection and clean-up are separate services. See to it you recognize which one you are obtaining, if cleanup is included or prices additional, and if a genuine person will examine your site.
5 Is support human, and just how quick?
During an incident you require a person. Inspect feedback time dedications, hours of coverage, and whether support can look at your site or respond to generic concerns.
6 Does it collaborate with how you handle the site?
If you take care of numerous websites, search for devices with centralized monitoring. If you make use of staging and release process, make sure setting regulations do not conflict with them. If you manage sites using the command line, bear in mind that updates can be done with WP-CLI , and your protection devices must function smoothly keeping that.
7 Does it assist you prevent over-installing?
Utilizing 3 safety and security plugins does not give you three times the protection. Overlapping firewalls and scanners can contrast, develop replicate alerts, and reduce your website. It is far better to have one well-integrated setup than a mix of many plugins.
WordPress safety plugins vs. WordPress safety solutions: which do you need?
A plugin is software you mount and run. A WordPress safety and security solution is an ongoing setup where another person deals with component of the work– usually surveillance, firewall software operation, and malware cleanup.
A plugin makes good sense when you have the time and convenience degree to evaluate alerts, apply updates promptly, analyze scan outcomes, and tidy up an infection if one occurs.
A solution makes good sense when downtime has genuine price, when nobody on your group wishes to be in charge of malware removal at 2 a.m., when you take care of sites for clients, or when you have already been hacked when and do not intend to duplicate the experience.
Actually, many secure WordPress sites utilize both a plugin for hardening and presence inside WordPress, and an exterior firewall program and monitoring solution for filtering system, uptime checks, blocklist tracking, and clean-up. This split strategy is what Sucuri uses: a WordPress plugin for solidifying and keeping track of, a cloud firewall before the site, and cleaning assistance if something gets through.
One caution when comparing paid choices: read what “limitless cleanings” or “assured elimination” suggests in the actual terms, including reaction times and what happens with websites on unsupported or heavily tailored hosting.
WordPress safety and security checklist
A plugin must follow other actions, not be your very first relocation. Here is the list we suggest for any kind of website owner.
Accessibility and accounts
- Audit every user account. Eliminate accounts nobody uses. Devalue any person that does not need Manager.
2 Implement solid, distinct passwords for each account with control panel access, including your host, registrar, and email.
3 Enable two-factor verification for all administrator accounts.
4 Rotate verification tricks and salts in wp-config. php, which invalidates existing sessions.
5 Use key-based verification instead of passwords for SFTP and SSH where your host supports it. See improving file transfer safety with SSH crucial authentication
Software application
- Update WordPress core, plugins, and themes on a defined routine. Enable automated updates for core safety and security releases at minimum.
7 Remove shut off plugins and extra styles. Deactivated code is still code on disk. Our overview to bookkeeping and tidying up WordPress plugins and themes goes through this.
8 Eliminate any nulled or pirated plugin or style right away and deal with the website as potentially jeopardized.
9 Only mount software from the official repository or the vendor straight, and examine that it is still proactively preserved.
Setup and hardening
- Appropriate data and directory authorizations; nothing ought to be world-writable.
11 Disable the integrated plugin and style documents editor.
12 Block PHP execution in/ wp-content/uploads/.
13 Disable XML-RPC if absolutely nothing you use depends on it.
14 Serve the entire site over HTTPS and confirm there are no mixed-content warnings.
15 Solidify any kind of public kinds versus abuse. Our blog post on best techniques for web kind safety covers spam, shot, and validation.
Discovery
- Run set up malware and integrity scans, and make sure informs reach an inbox a person checks out.
17 Monitor for blocklist standing so you learn about a trouble before your site visitors do.
18 Keep an eye on individual production and plugin activation occasions in your activity log.
Filtering and healing
- Put a firewall before the website so harmful website traffic is filteringed system before it reaches your server.
20 Take automated, off-server, versioned back-ups of documents and data source, then examine a bring back.
21 List your event steps currently: who to contact, where qualifications live, just how to take the site offline.
If you just adhere to 10 of these actions, begin with the account, update, and back-up jobs. These protect against even more problems than any kind of solitary plugin setup.
What are the WordPress safety best practices that matter most long-lasting?
Tools can become outdated, yet excellent routines last.
- Deal with updates as a routine, not an interruption: Pick a day. Update on hosting if you have one. One of the most typical origin of concession is a recognized vulnerability that had a patch available.
- Limit the number of plugins you make use of: Each plugin is added code keeping up your site’s approvals. Using less, well-maintained plugins is important for both safety and efficiency.
- Think least benefit almost everywhere: Contributors do not need Manager. Your database customer does not need permissions it never ever makes use of. Your CI token does not require create accessibility to every little thing.
- Different atmospheres and credentials: Organizing must not share credentials with manufacturing. Designers that leave ought to lose accessibility the exact same day.
- Ensure someone in fact reviews your surveillance notifies: If nobody checks them, they are not helpful. Send out notifies to a noticeable area and appoint a person to handle them.
- Technique restoring your site: Restore a backup in a test setting every couple of months. You do not want your very first restore to occur during a real emergency.
- List vital information: Like where your DNS is handled, that possesses the registrar account, what your organizing strategy covers, and which plugins are necessary for your service. Incidents commonly take longer to fix since this information is hard to locate.
- Don’t count on just concealing things: Concealing your login URL or WordPress version only makes it a little bit harder for fundamental scans, but it is unreal security. Always prioritize patching, strong credentials, and correct filtering.
Is a totally free WordPress safety plugin enough?
Free plugins do a great deal of truly useful work: solidifying, documents honesty surveillance, activity logging, basic malware scanning, and login defense. For a low-risk personal or pamphlet website with excellent upgrade technique and off-server backups, a cost-free plugin plus solid practices is a reasonable standard. The Sucuri WordPress plugin is complimentary for specifically this reason.
Where cost-free tiers normally stop:
- Filtering system prior to traffic hits your server: Running framework in front of your site prices cash to operate, so it is seldom totally free.
- Rapid protection against newly revealed vulnerabilities: Regulation updates that get here rapidly, and digital patching that shields a susceptible plugin prior to you can upgrade it, normally rest behind a paid rate.
- Removal: Free devices inform you there is malware. Cleaning it , including searching for every backdoor, not just the visible sign, is labor.
- Human support throughout an event: Community online forums are not an occurrence response channel.
- Blocklist elimination and online reputation tracking: Obtaining delisted by online search engine and web browser suppliers includes procedure job.
To be clear, totally free devices mean you need to do more of the job yourself. This is fine if you have the moment and abilities, however not a great idea if your site generates income and you lack the competence.
The number of safety plugins should you go for once?
In practically every case, you must make use of simply one safety plugin, together with different devices for back-ups and, ideally, a firewall program that is not a plugin.
Making use of two safety suites can create real issues. Two firewall programs may examine the very same requests and have conflicting policies. Two scanners might flag each other’s data as threats. Two login protection tools can secure you out or break password resets. Obtaining replicate alerts can likewise make you ignore them.
If you change plugins, see to it to shut off and entirely eliminate the old one first. Additionally, inspect that any kind of modifications it made, like.htaccess regulations, consents, login URL modifications, or database tables, have been reversed. Leftover policies from old plugins commonly cause problems that are difficult to diagnose.
For a lot of sites, we advise making use of one plugin for setting and keeping an eye on inside WordPress, a firewall software in front of your site, a back-up solution that stores duplicates off the web server, and a clear plan for that handles what happens if something fails.
Frequently asked questions
Do I need both a safety and security plugin and a WAF?
For many sites, yes. A plugin sets WordPress and detects changes from the inside, but it just pursues WordPress loads. A internet application firewall program filters malicious requests before they reach your web server, absorbing assault website traffic and remaining operational even if the website itself is jeopardized. They cover various layers.
What’s the difference in between a WordPress safety plugin and a server-level firewall program?
A plugin runs inside WordPress, so protection takes place after PHP and WordPress have actually currently filled and taken in web server sources. A server-level or cloud firewall sits in front of your website and goes down harmful requests upstream. Since it lives outdoors your installment, an opponent with documents access can not disable it.
Can release WordPress safety and security plugins secure versus zero-days?
Only partially. A zero-day is a flaw without spot available yet, so free plugins can provide setting and detection but hardly ever fast regulation updates or online patching. Filtering that obstructs exploitation prior to a vendor releases a fix normally needs a conserved firewall service, not a totally free plugin alone.
What should get on a WordPress security checklist?
Audit individual accounts and apply two-factor authentication, update core, plugins, and motifs on a schedule, erase extra expansions, repair documents approvals, disable the documents editor, block PHP in uploads, serve every little thing over HTTPS, run set up malware scans, placed a firewall before the website, and examination off-server back-ups.
Are WordPress safety and security plugins bad for website efficiency?
They have a cost, but it is convenient. Checking files, checking demands, and writing task logs all eat server resources, and boundless log tables can bloat your data source. Tune scan timetables and log retention, prevent running 2 overlapping suites, and favor filtering system that occurs prior to traffic reaches your web server.
Do I still require a safety plugin if my host claims it handles protection?
Generally yes. Taken care of hosts often patch the web server, limit some file composes, and deal fundamental malware scanning, however coverage varies commonly and the majority of do not remediate infections in your WordPress documents. Ask your host in writing what is monitored, what is filteringed system, and what occurs if your website is jeopardized.
What’s the distinction between a WordPress protection plugin and a WordPress safety service?
A plugin is software application you install and operate on your own. You assess signals, use solidifying, and take care of cleaning. A solution is a recurring arrangement where a service provider runs the firewall, monitors the site, and remediates malware. Many websites utilize both: a plugin for in-WordPress visibility, a solution for filtering and feedback.